Govern AI Use Across the Enterprise
Leadership gets a clear answer to where AI is used, what data it touches, who approved it and how risk is monitored, through one model spanning policy, risk, legal, security, privacy and procurement, run on the Hicomply compliance platform.
AI Governance Capabilities
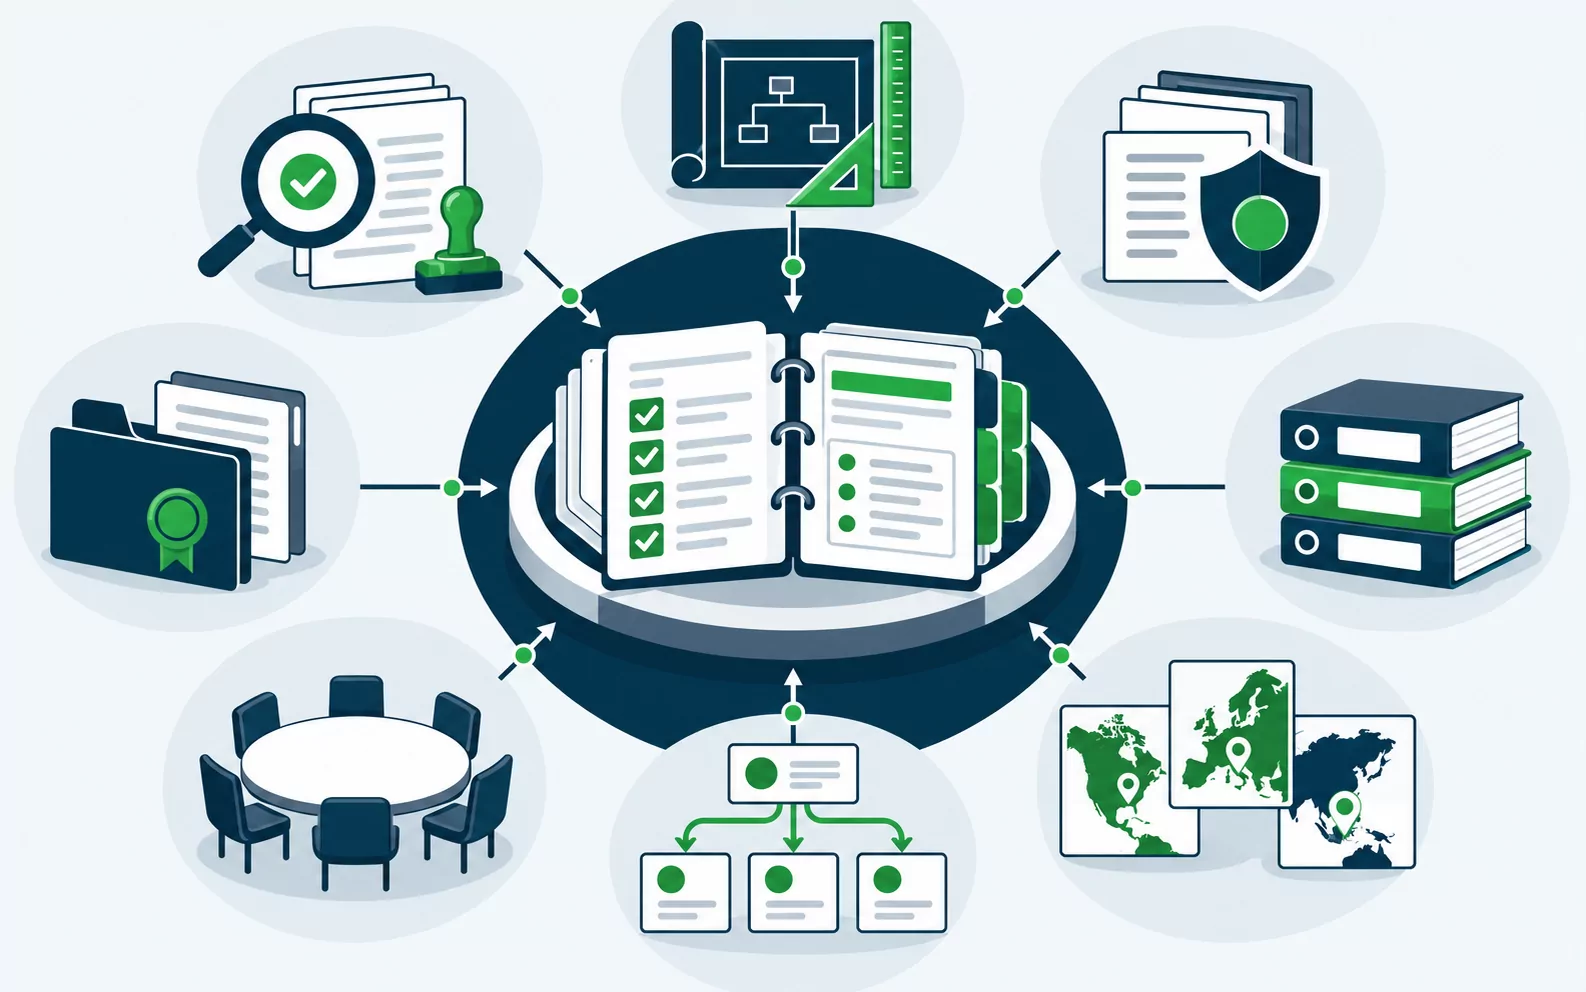
Every capability is delivered on the Hicomply compliance platform, so the AI inventory, risk assessments, policies, approvals and evidence stay in one governed system aligned to ISO/IEC 42001.
Enterprise AI inventory and use-case discovery
Risk classification and assessment models
AI policy, standards, and acceptable-use guidance
Intake, review, approval, and exception workflows
Roles, committees, and accountability models
Third-party AI and procurement controls
Data, privacy, security, and human oversight requirements
Model tracking and use-case lifecycle governance
Monitoring, incident, and change management processes
ISO/IEC 42001 evidence, reporting, and audit readiness
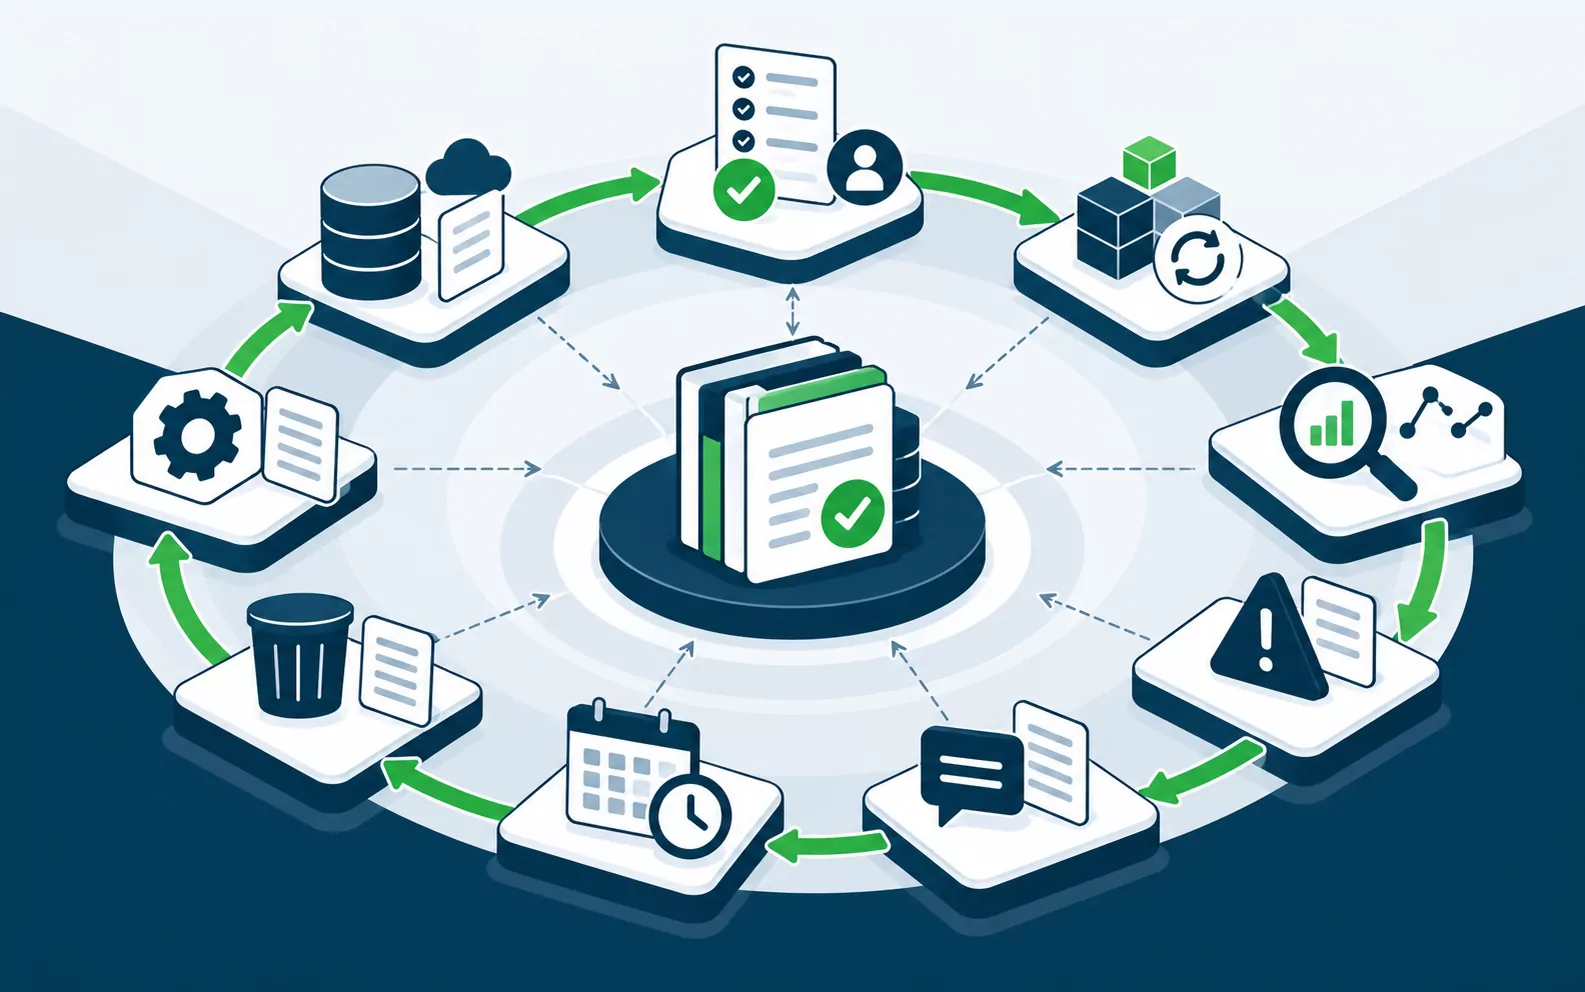
Governed AI Lifecycle
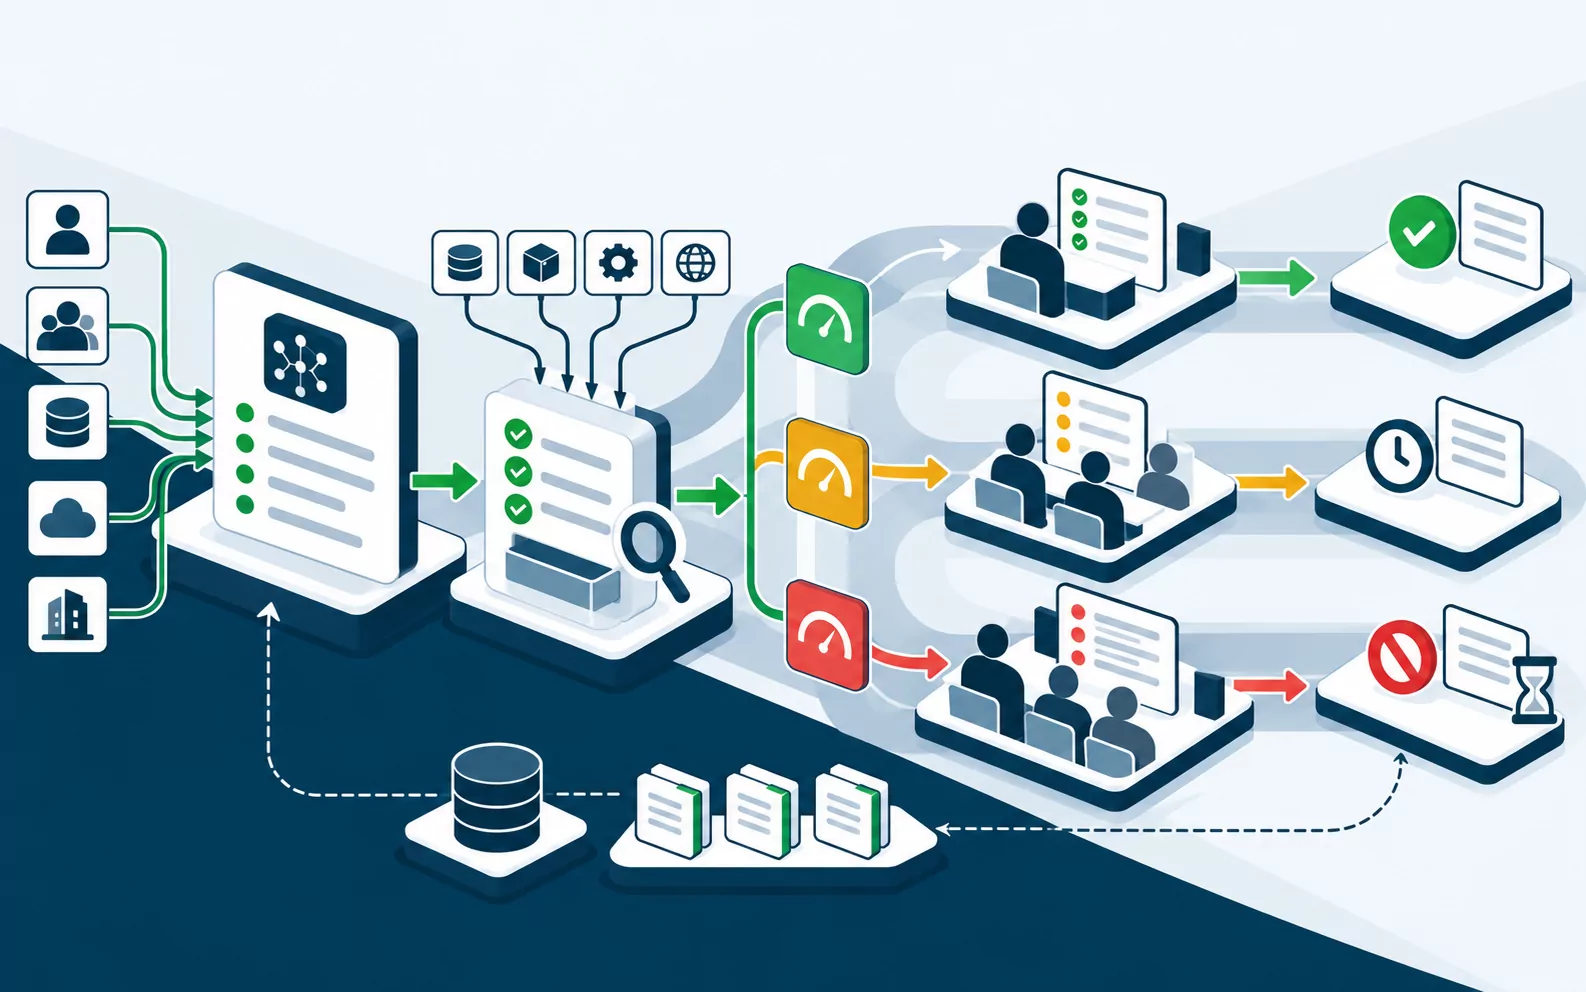
Every AI use case moves from intake and risk classification through approval, operation, monitoring, change and retirement, with each stage recorded on the Hicomply platform.
Discover
Classify
Review
Approve
Monitor
Change or retire
Framework Alignment
AI regulation is moving quickly and varies by market. Aligning to recognized frameworks gives leadership a defensible position today and a structure that adapts as obligations change.
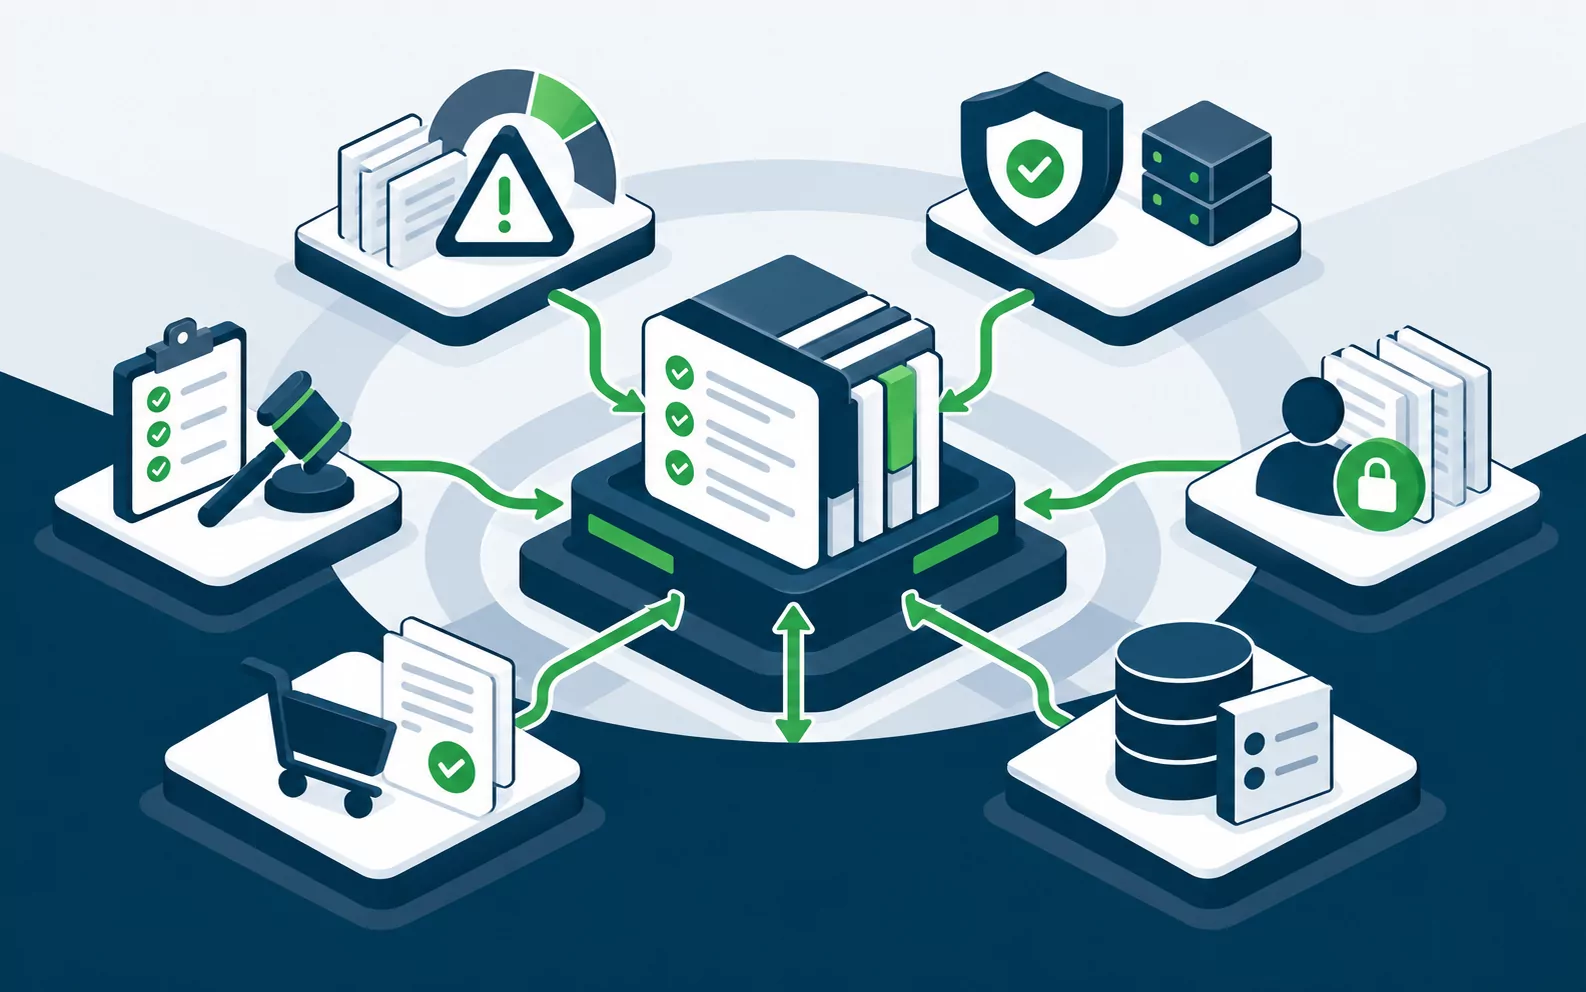
Governance programs align to ISO/IEC 42001, the NIST AI Risk Management Framework and, where applicable, the EU AI Act, along with regional, sector and contractual requirements. The ISO/IEC 42001 AI management system is implemented on the Hicomply platform, alongside ISO/IEC 27001:2022 where an information security management system already exists. Formal legal interpretation remains with qualified legal counsel.
Assessment of applicable AI regulations and frameworks
ISO/IEC 42001 AI management system implementation on Hicomply
NIST AI RMF and EU AI Act alignment, where applicable
AI policy, standards and acceptable-use guidance
Certification readiness support
How an Engagement Progresses
Discover and Baseline
AI use across embedded features, employee tools, vendor services and development platforms is inventoried in Hicomply, with owners and a gap analysis against ISO/IEC 42001.
Classify and Design
Risk tiers, policies, intake criteria and decision rights are configured on the platform and mapped to existing security, privacy and risk controls.
Operate the Intake Path
New and changed AI uses move through risk-based review and approval on the platform, with evidence captured at every decision.
Monitor and Audit
Continuous monitoring, periodic reviews and internal audits keep the AI management system audit-ready for ISO/IEC 42001 and customer assurance reviews.
A Governance Path for Every AI Use Case, From Intake to Renewal
Outputs give the enterprise a single AI inventory, a risk-based review path, and clear decision rights built on existing governance, all maintained on the Hicomply platform.
Enterprise AI inventory and ownership model
Risk classification methodology and assessment templates
AI policy, standards, acceptable-use, and third-party due-diligence requirements
Intake, review, approval, exception, and renewal workflows
Governance roles, committee charters, and decision rights
Lifecycle monitoring, incident, change, and reporting processes, with a phased implementation roadmap
Hicomply platform licensing, configuration and onboarding for the AI management system
Governance That Enables Responsible AI
Visibility into enterprise AI use
Consistent risk-based decisions
Clear ownership and approval requirements
Timestamped evidence for customers, auditors, and regulators
A roadmap for improving governance maturity
A practical foundation for responsible AI adoption
Related Services
AI Security
AI applications and agents assessed and protected across every connection they reach.
Explore AI SecurityGovernance Risk and Compliance
One control framework that satisfies multiple obligations with evidence from daily operations.
Explore Governance Risk and ComplianceIntelligent Automation and Agentic AI
Automation with clear boundaries, human approval and measured results.
Explore Intelligent Automation and Agentic AI