Make Compliance Part of the Operating Model
Obligations become owned controls, operating processes and evidence gathered through daily work on the Hicomply compliance platform, so audit readiness is continuous rather than a pre-audit scramble.
Governance Risk and Compliance Capabilities
Every capability is delivered on the Hicomply compliance platform, so assessments, policies, risks, controls and evidence stay in one governed system that keeps running after implementation.
Current-state and readiness assessments
Control framework design and rationalization
Policy, standard, and procedure development
Risk registers and treatment planning
Third-party and vendor risk management
Control ownership and evidence models
Hicomply platform implementation and compliance workflows
Audit preparation and remediation support
Continuous control monitoring and alerting
Executive and board-level risk reporting
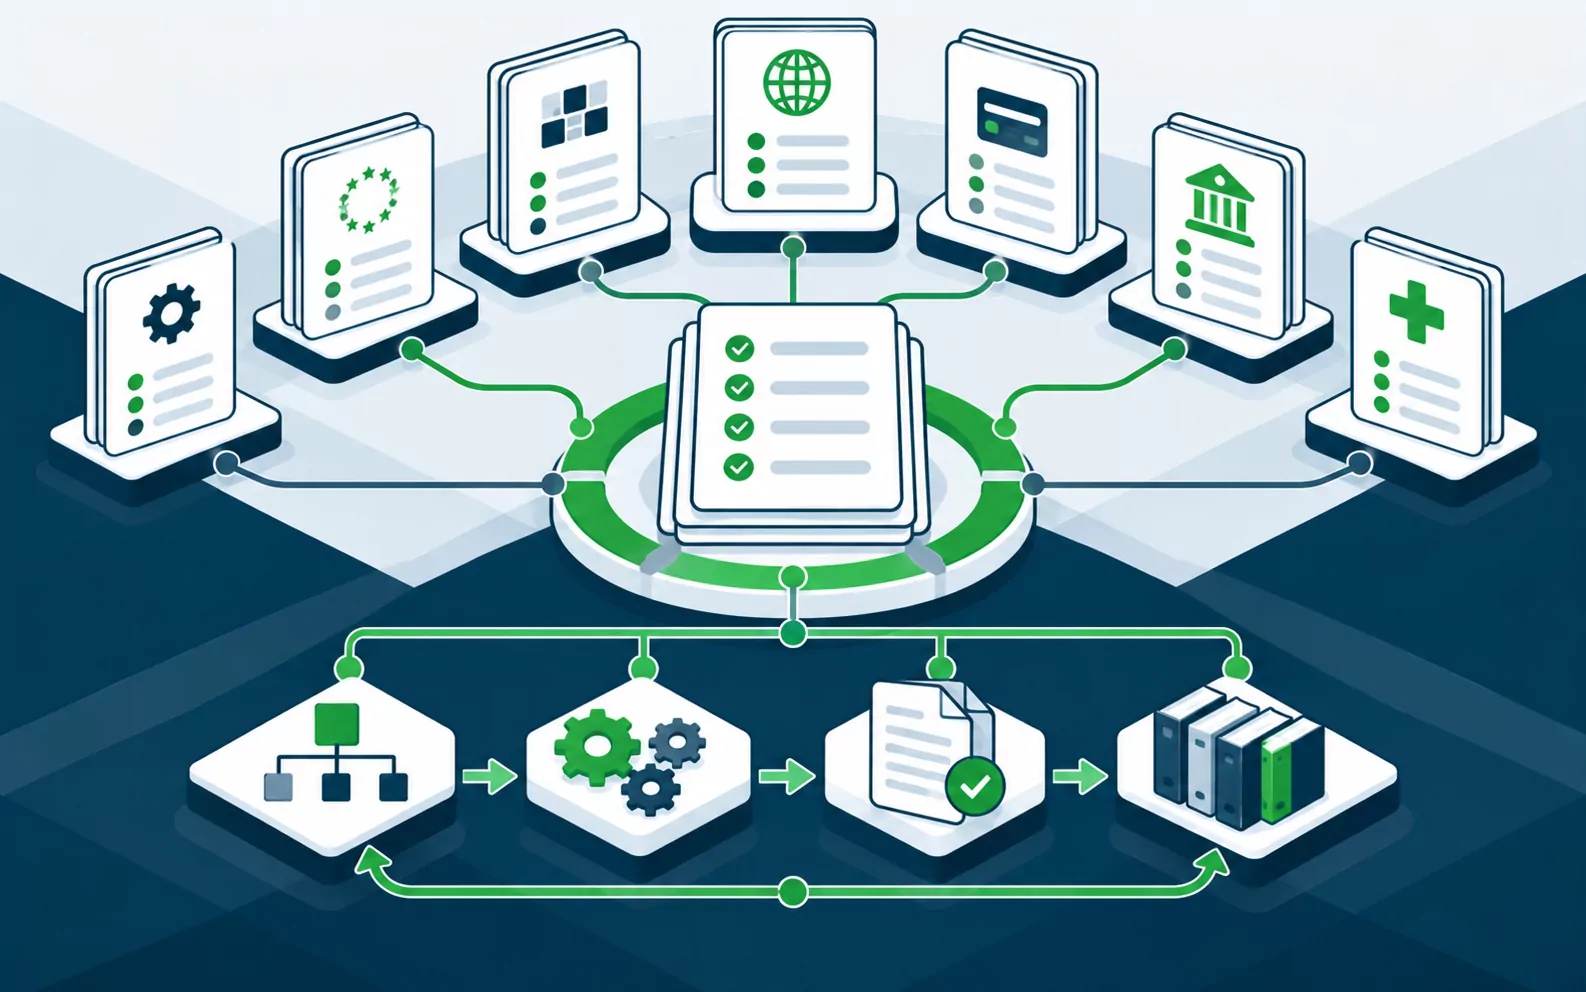
Enterprise Control Lattice
Connect obligations, risks, shared controls, accountable owners, systems, evidence, and remediation decisions in one operating view, maintained on the Hicomply platform.
Obligations
Risks
Controls
Owners
Evidence
Improvement
Framework and Regulatory Alignment
Most organizations answer to several frameworks at once. Aligning them in one program avoids duplicate effort and gives auditors, customers and regulators a consistent answer.
Engagements address ISO/IEC 27001:2022, SOC 2, NIST CSF 2.0 and SP 800-53, GDPR, ISO/IEC 27701:2025, PCI DSS v4.0.1, DORA, and applicable HIPAA, regional or sector requirements, with each control set managed on the Hicomply platform. Scope reflects the client’s jurisdiction, industry, contracts and certification objectives, and interpretation is coordinated with the client’s legal and compliance stakeholders.
Gap assessment against selected frameworks and regulations
Scope definition and certification readiness roadmap
Policy and procedure development
Hicomply platform licensing, configuration and onboarding
Internal audit and external audit preparation support
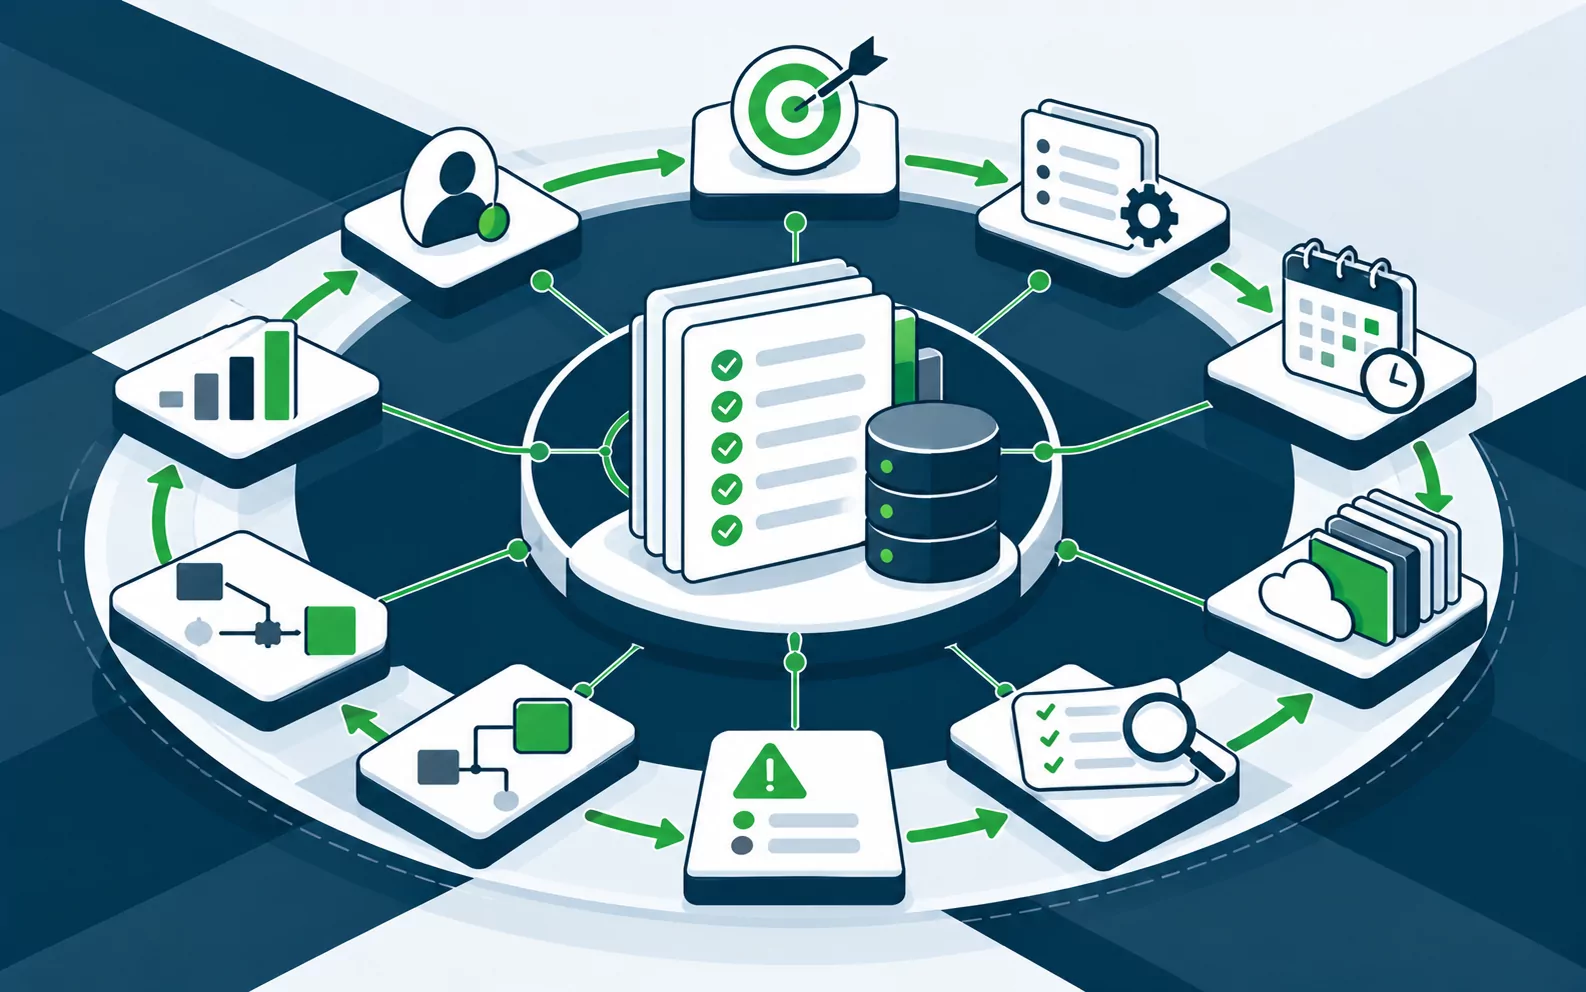
How an Engagement Progresses
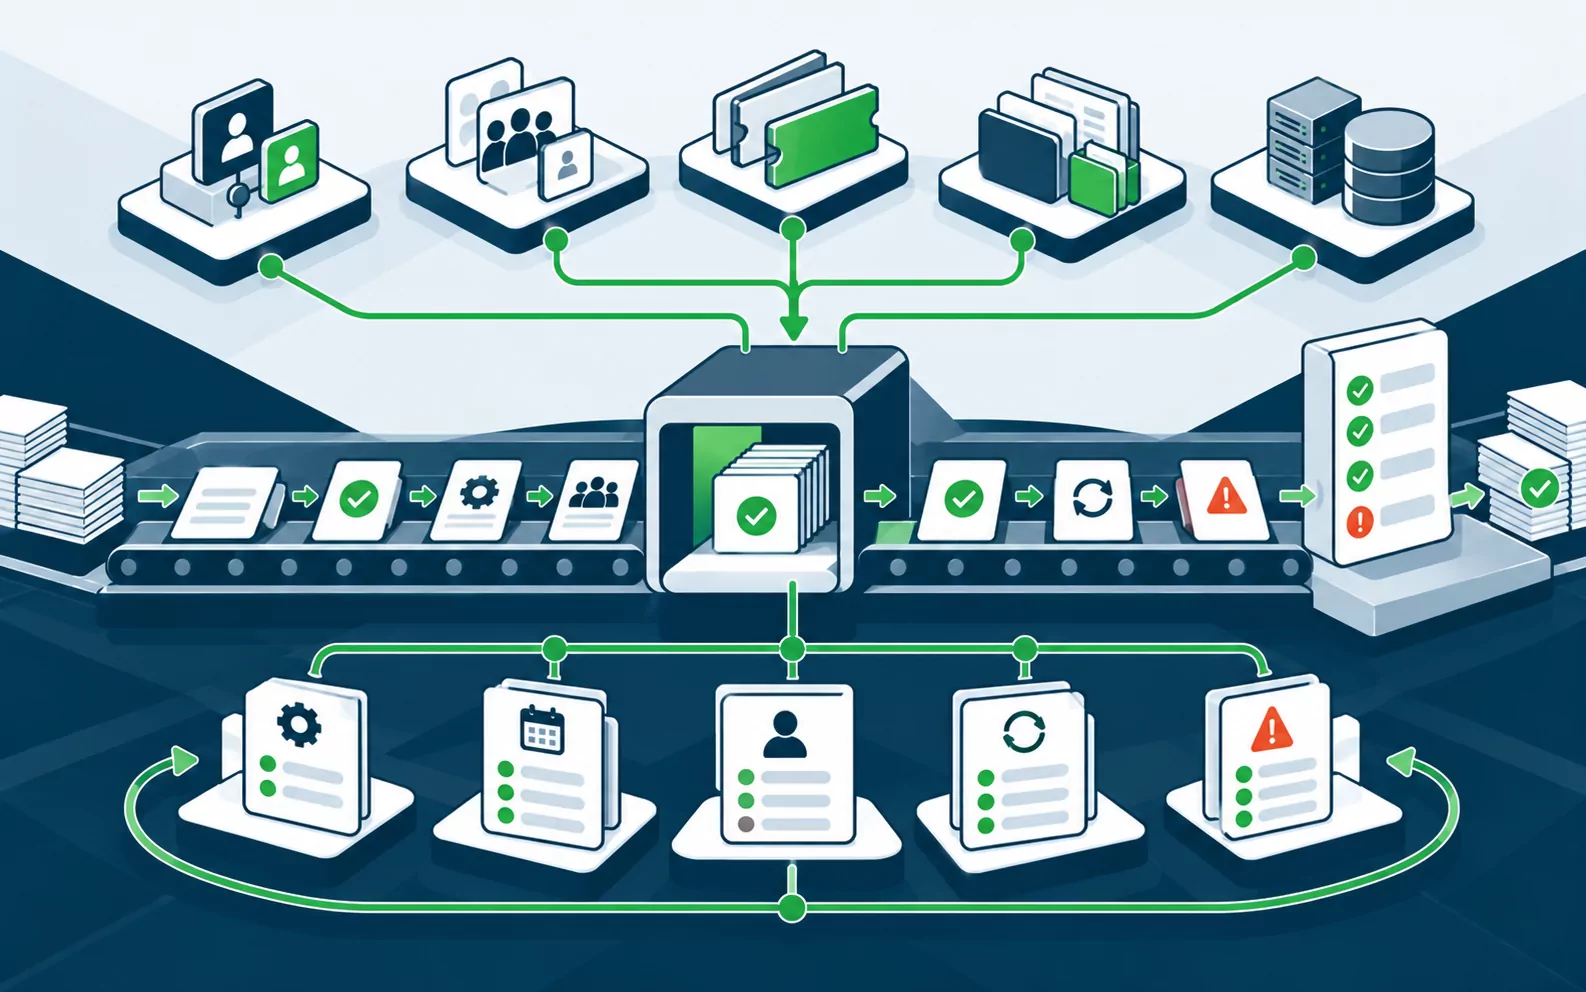
Scope and Baseline
The ISMS scope, obligations, information assets and current controls are captured in Hicomply, producing a gap analysis and a prioritized baseline.
Design and Implement
Common controls, policies, risk assessments and ownership are configured on the platform and mapped across every framework in scope.
Integrate and Evidence
Identity, HR, ticketing and file-storage systems are connected, so evidence is collected automatically and linked to the controls it supports.
Audit and Operate
Internal audits, readiness reviews and continuous control monitoring keep the program audit-ready between certification cycles.
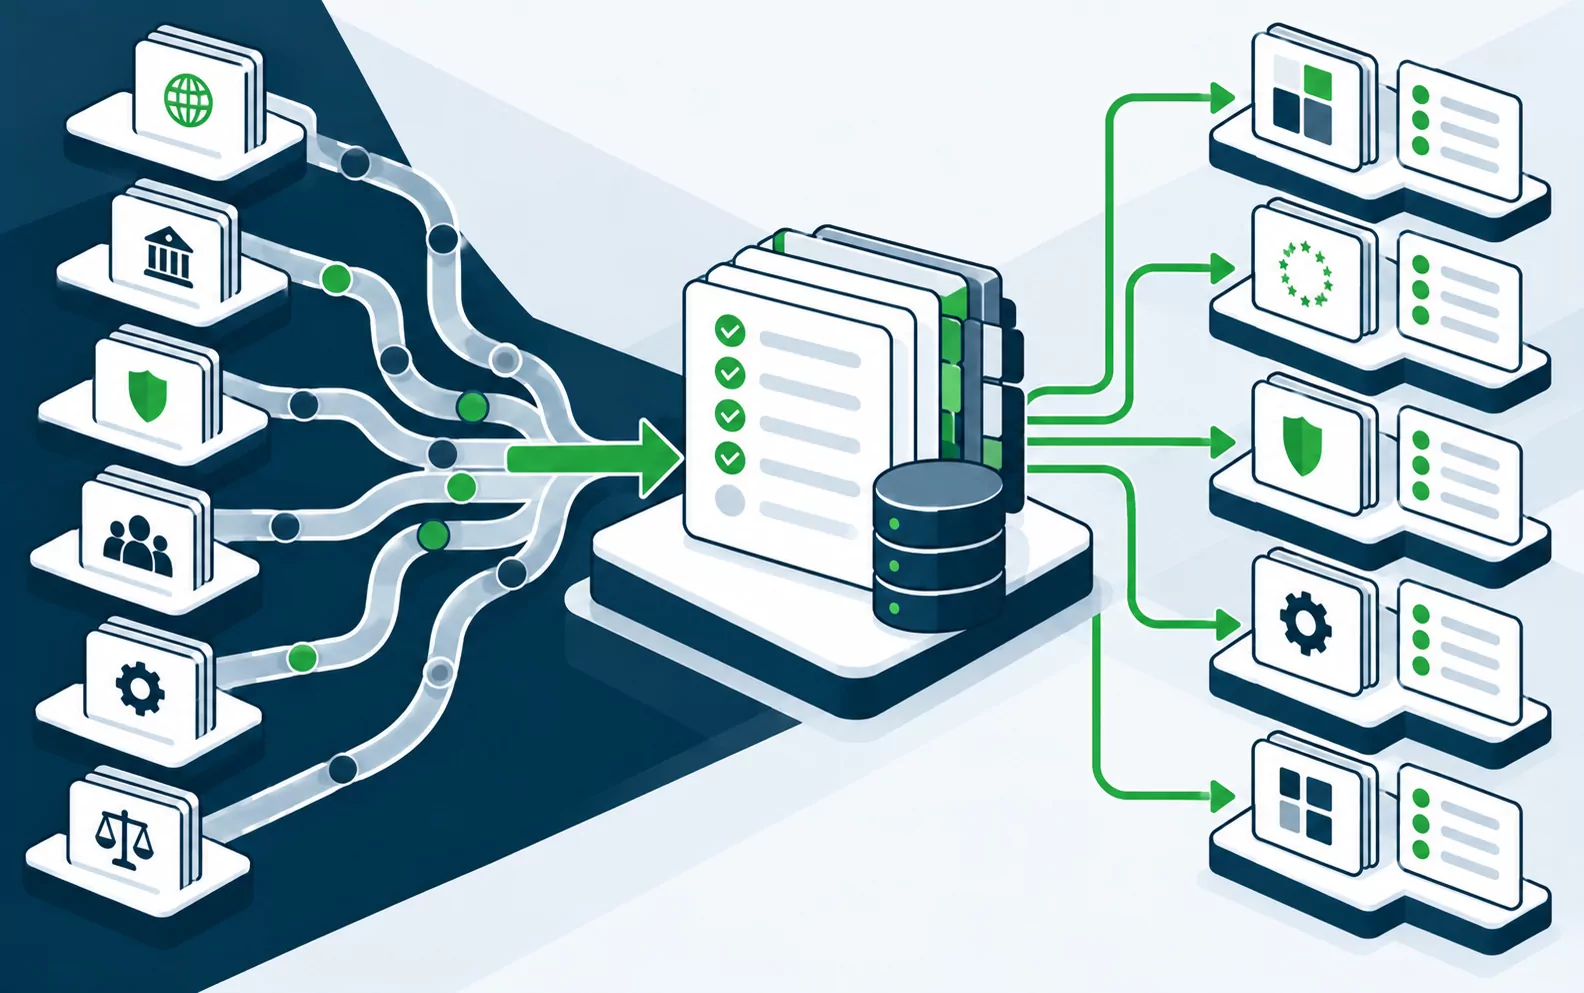
One Control System Mapped to Every Obligation You Carry
Outputs connect obligations to controls, controls to evidence, and evidence to executive and audit reporting, all maintained on the Hicomply platform.
Obligation inventory and control crosswalk
Risk and control baseline with prioritized gaps
Policies, standards, procedures, and ownership model
Evidence catalog and collection workflow
Third-party risk process and assessment criteria
Remediation roadmap, governance cadence, and executive and audit-ready reporting definitions
Hicomply platform licensing, configuration and onboarding
Compliance That Holds Up Between Audits
Clear accountability for controls and risks
Reduced duplication across overlapping frameworks
Better audit readiness and evidence quality
More consistent third-party risk decisions
A prioritized remediation roadmap
Governance that keeps running on the platform after implementation
Related Services
AI Governance and Compliance
A governed path for every AI use case, from intake to renewal.
Explore AI Governance and ComplianceManaged Security Services
Defined security coverage, escalation and reporting that extend the internal team.
Explore Managed Security ServicesServiceNow Implementation
ServiceNow configured around the operating model and released in measurable phases.
Explore ServiceNow Implementation